penetrify.cloud/blog
Blog
Insights, guides et actualités à la pointe de la sécurité autonome.
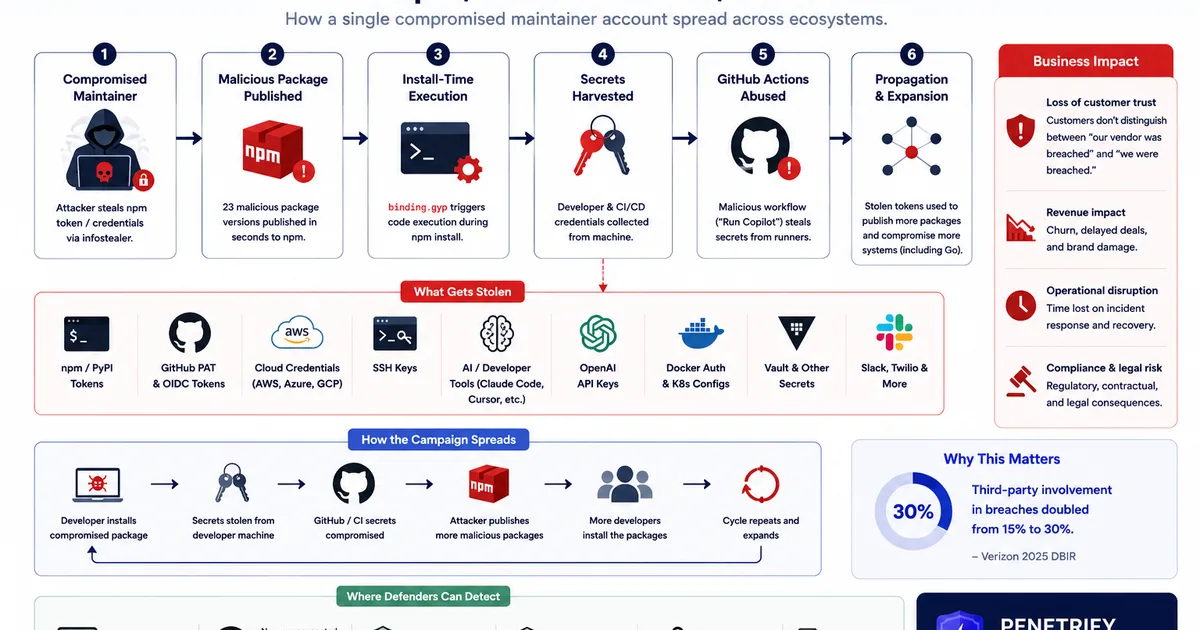
Au cœur de Miasma : comment un seul compte npm compromis a déclenché une attaque de la chaîne d'approvisionnement multi-écosystème
En juin 2026, un seul jeton npm volé a débouché sur 23 paquets LeoPlatform trojanisés, un workflow GitHub Actions malveillant et un module Go compromis. Aucune CVE n'est intervenue à aucune étape. Voici ce qui s'est passé, où les défenseurs auraient pu l'intercepter, et pourquoi l'analyse des dépendances n'avait aucune chance d'y parvenir.

Nous avons réussi toute la suite de benchmarks XBOW — dans notre palier le plus rapide
Notre moteur de pentest autonome a résolu les 104 défis d'exploitation web XBOW (XBEN) — 100 % — en utilisant notre palier de scan le plus rapide et le moins cher. Voici le résultat, la méthode et les réserves honnêtes.
Le trou dans les correcteurs de CVE-Bench : quand des exploits réussis obtiennent zéro
Plusieurs des correcteurs automatisés de CVE-Bench plantent ou se figent dès qu'un exploit perturbe sa cible, et un correcteur planté est silencieusement enregistré comme une attaque échouée. Le benchmark peut noter une compromission authentique comme un échec.
SQL Injection Despite the ORM: The One Raw Query Nobody Reviewed
Using an ORM does not prevent SQL injection. It concentrates it: hundreds of safe queries lull the team, and the one raw query someone wrote for a report interpolates a parameter straight into the statement.
Indirect Prompt Injection to Data Exfiltration: When the Model Has Tools
Prompt injection on its own is a curiosity. Prompt injection reaching a tool that holds real credentials is a breach — and the instruction does not have to come from your user. It can arrive inside the document your app was asked to summarise.
The Unverified Stripe Webhook: Forging checkout.session.completed for Free Premium
Your webhook endpoint is a public URL that grants entitlements. Without signature verification it accepts a payment confirmation from anyone — and the request that upgrades an attacker to your top tier is a single curl command.
When org_id Is a Parameter, Not a Boundary: Multi-Tenant Data Isolation Failure
Every multi-tenant application has an organisation identifier. The question that decides whether you have isolation is where it comes from — the session, or the request. When it comes from the request, one customer reads another's data with a single edited value.
Firebase Security Rules Left Wide Open: allow read, write: if true
Firebase asks you to choose a rules mode when you create a database, and the permissive option is the one that makes the tutorial work. Months later the app is live, the rule still says if true, and anyone with the project ID can read and write the entire database.
The Supabase service_role Key in the Client Bundle: RLS Bypassed Entirely
Row Level Security is the control that keeps one Supabase user out of another's rows. The service_role key is designed to ignore it. When that key reaches the browser, every policy you wrote stops mattering — and the pattern shows up in production more often than anyone admits.
Notre propre application stockait les jetons d'authentification dans localStorage. Voici ce que nous avons changé.
Nous avons scanné notre application : le rapport a signalé la connexion Cognito. Pourquoi le chiffrement n'y change rien et ce que nous avons livré à la place.