penetrify.cloud/blog
Blog
Insights, guides, and updates from the forefront of autonomous security.
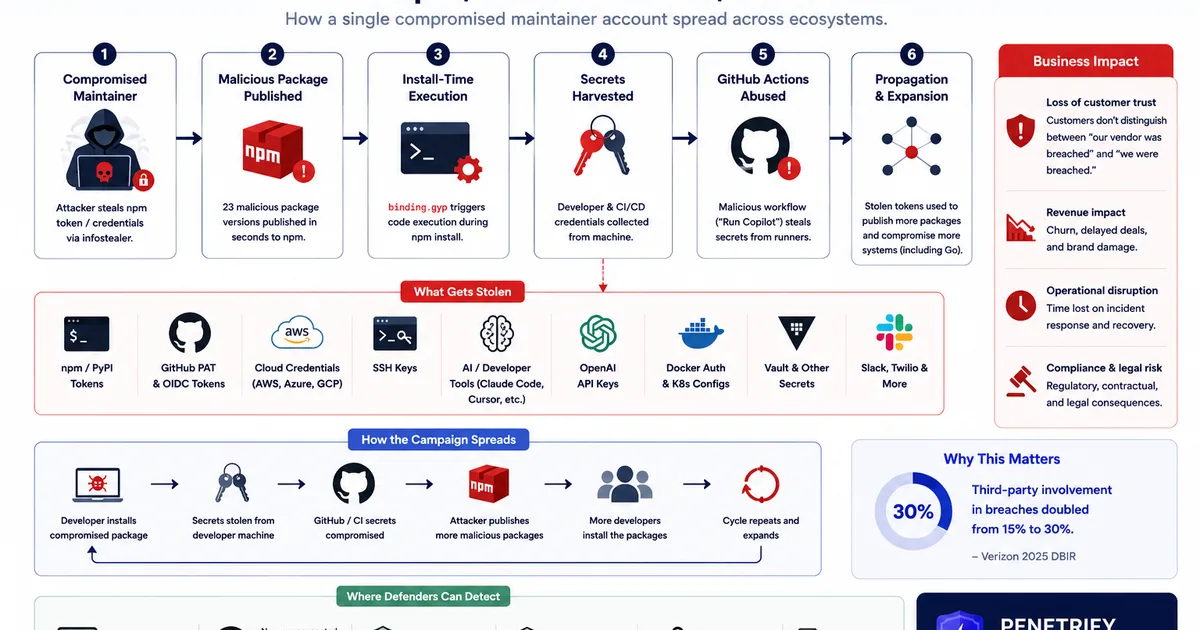
Inside Miasma: How One Compromised npm Account Turned Into a Multi-Ecosystem Supply Chain Attack
In June 2026 a single stolen npm token turned into 23 trojanized LeoPlatform packages, a malicious GitHub Actions workflow and a compromised Go module. No CVE was involved at any step. Here is what happened, where defenders could have caught it, and why dependency scanning was never going to.

We Cleared the XBOW Benchmark Suite — in Our Fastest Tier
Our autonomous pentest engine solved all 104 XBOW (XBEN) web-exploitation challenges — 100% — using our fastest, cheapest scan tier. Here's the result, the method, and the honest caveats.
The CVE-Bench Grader Gap: When Successful Exploits Score Zero
Several of CVE-Bench’s automated graders crash or hang the moment an exploit disrupts its target, and a crashed grader is silently recorded as a failed attack. The benchmark can score a genuine compromise as a failure.
SQL Injection Despite the ORM: The One Raw Query Nobody Reviewed
Using an ORM does not prevent SQL injection. It concentrates it: hundreds of safe queries lull the team, and the one raw query someone wrote for a report interpolates a parameter straight into the statement.
Indirect Prompt Injection to Data Exfiltration: When the Model Has Tools
Prompt injection on its own is a curiosity. Prompt injection reaching a tool that holds real credentials is a breach — and the instruction does not have to come from your user. It can arrive inside the document your app was asked to summarise.
The Unverified Stripe Webhook: Forging checkout.session.completed for Free Premium
Your webhook endpoint is a public URL that grants entitlements. Without signature verification it accepts a payment confirmation from anyone — and the request that upgrades an attacker to your top tier is a single curl command.
When org_id Is a Parameter, Not a Boundary: Multi-Tenant Data Isolation Failure
Every multi-tenant application has an organisation identifier. The question that decides whether you have isolation is where it comes from — the session, or the request. When it comes from the request, one customer reads another's data with a single edited value.
Firebase Security Rules Left Wide Open: allow read, write: if true
Firebase asks you to choose a rules mode when you create a database, and the permissive option is the one that makes the tutorial work. Months later the app is live, the rule still says if true, and anyone with the project ID can read and write the entire database.
The Supabase service_role Key in the Client Bundle: RLS Bypassed Entirely
Row Level Security is the control that keeps one Supabase user out of another's rows. The service_role key is designed to ignore it. When that key reaches the browser, every policy you wrote stops mattering — and the pattern shows up in production more often than anyone admits.
Our own app stored auth tokens in localStorage. Here's what we changed.
We scanned our own app and the report flagged our Cognito login. Why encrypting localStorage wouldn't fix it, what we shipped instead, and how to check yours.